Type and progress
Personal architecture project in progress, September 2026–August 2027. The scope below describes the target design; it does not represent an infrastructure already deployed in production.
Challenge
Design a complete target architecture spanning governance, networks, identity, data, applications, detection, resilience and AI-enabled use cases.
My role
Target architecture, document governance, risk, WBS/baseline, controls and validation.
Key decisions
- Build the traditional cybersecurity foundation before AI extensions.
- Treat models, data, agents, tools and memories as governed assets.
- Design validation, evidence, recovery and handover from the outset.
Public deliverables
- Target architecture
- Information security policy and supporting policies
- Work breakdown structure, milestones and schedule baseline
- AI Security and Agentic AI Security dossiers
- Validation and handover plan
Public confidentiality rule.
This public page intentionally omits client-sensitive data, exploitable architecture details, internal configurations and proprietary or patent-oriented mechanisms.
This public page intentionally omits client-sensitive data, exploitable architecture details, internal configurations and proprietary or patent-oriented mechanisms.
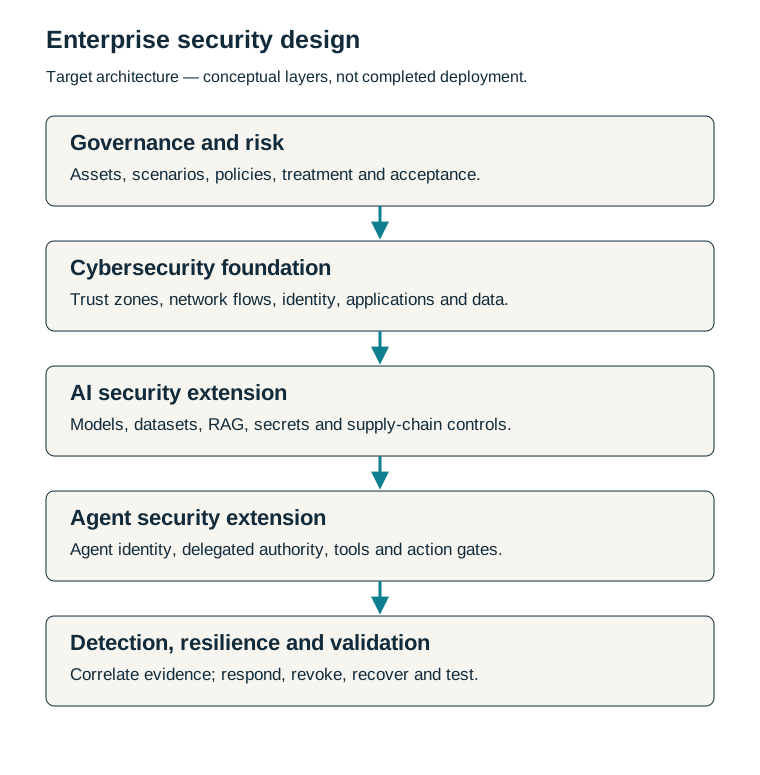
Governance and risk → Cybersecurity foundation → AI security extension → Agent security extension → Detection, resilience and validation